 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
#HTTPS
HTTPS is the encrypted version of HTTP that every modern website is expected to use. Articles tagged here explain how HTTPS protects visitors and what browsers do when it is missing or broken. They cover redirects from HTTP, mixed content, HSTS and moving an existing site to HTTPS. You will find step-by-step instructions for common servers, hosting panels and content management systems. Each guide also explains how to verify that the change really works. Use these articles whenever a browser shows a padlock problem or a Not Secure label.
 1 paź 2026 · Czas czytania: 8 min
SSL Private Keys: How to Store, Protect and Replace Them
Your SSL certificate is only as safe as its private key. Learn where keys should live, who may access them, and what to do…
 1 paź 2026 · Czas czytania: 8 min
Self-Signed SSL Certificates: When Are They Acceptable?
Self-signed certificates encrypt traffic but browsers do not trust them. Learn where they are acceptable, where they are risky, and the better free options.
 30 wrz 2026 · Czas czytania: 8 min
WWW or Non-WWW, Slash or No Slash: Pick One URL Version
WWW or not, trailing slash or not: search engines treat each variant as a separate URL. Learn how to pick one version, redirect the…
 29 wrz 2026 · Czas czytania: 7 min
TLS 1.3 Explained: Why It Is Faster and How to Enable It
TLS 1.3 makes HTTPS connections faster and removes weak cryptography. Learn what changed, how to check your server and how to enable it safely.
 24 wrz 2026 · Czas czytania: 8 min
How to Automate SSL Renewal With Certbot (and Verify It Works)
Set up Certbot so Let's Encrypt certificates renew automatically: timers, reload hooks, DNS challenges behind CDNs, dry runs and checks for silent failures.
 21 wrz 2026 · Czas czytania: 7 min
Domain Hijacking: How to Protect Your Domain Name and DNS
Losing control of your domain takes down your website and e-mail at once. Learn how domains get hijacked or expire and how to lock…
 15 wrz 2026 · Czas czytania: 8 min
How to Add Security Headers on Apache, Nginx, WordPress and CDNs
Copy-ready examples for adding HSTS, CSP, X-Frame-Options and other security headers on Apache, Nginx, WordPress hosting and CDNs, plus how to verify them.
 14 wrz 2026 · Czas czytania: 8 min
DNSSEC Explained for Website Owners: Is It Worth Enabling?
DNSSEC signs your DNS records so resolvers can detect forged answers. Learn how it works, what it protects, the risks of misconfiguration and how…
 7 wrz 2026 · Czas czytania: 8 min
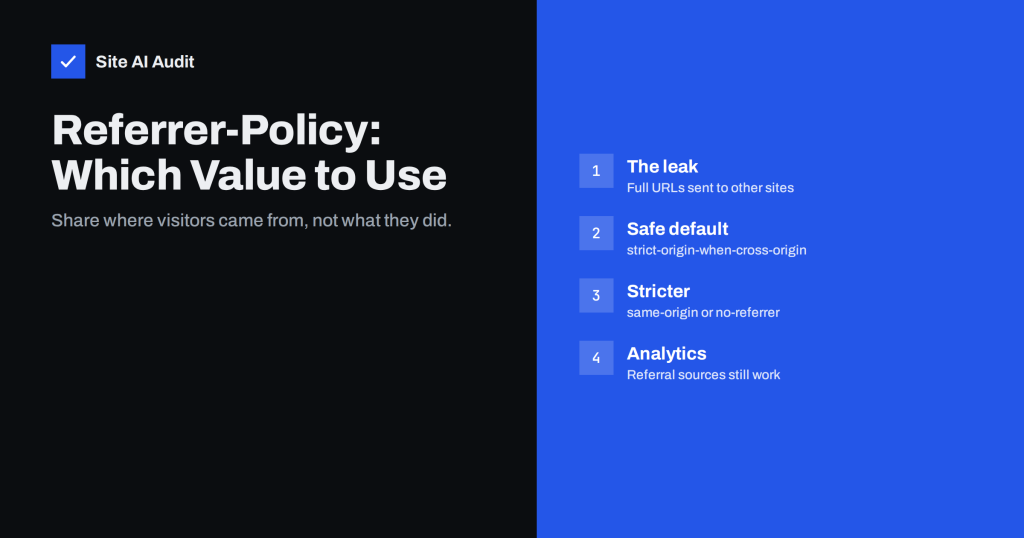
Referrer-Policy Header: Which Value to Use and Why It Matters
Referrer-Policy controls how much of your page URLs other sites see. Learn what each value does, the safe default, and how it affects analytics…
 6 wrz 2026 · Czas czytania: 7 min
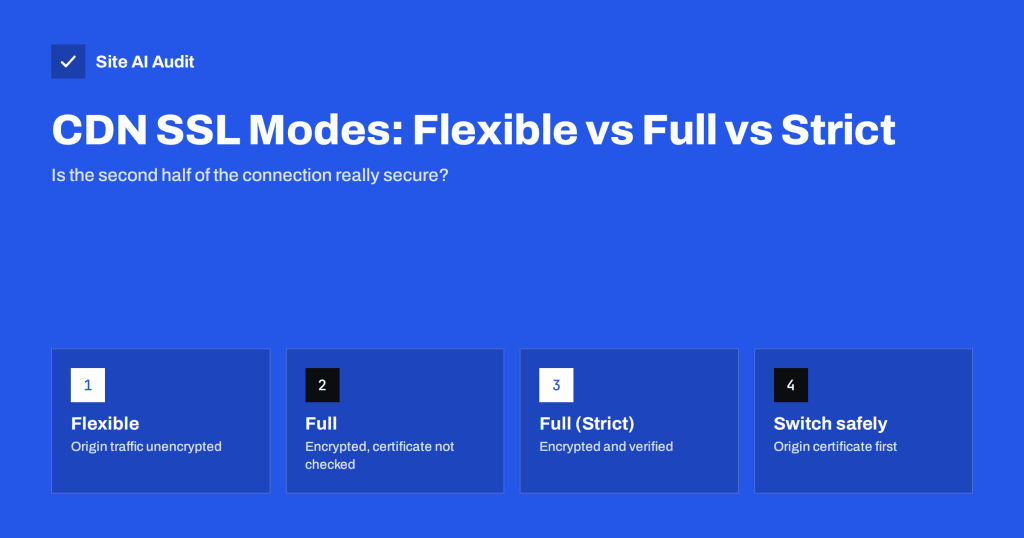
CDN SSL Modes Explained: Flexible vs Full vs Full (Strict)
Flexible, Full and Full (Strict) decide whether traffic between your CDN and server is encrypted and verified. Learn the risks and how to switch…
 3 wrz 2026 · Czas czytania: 8 min
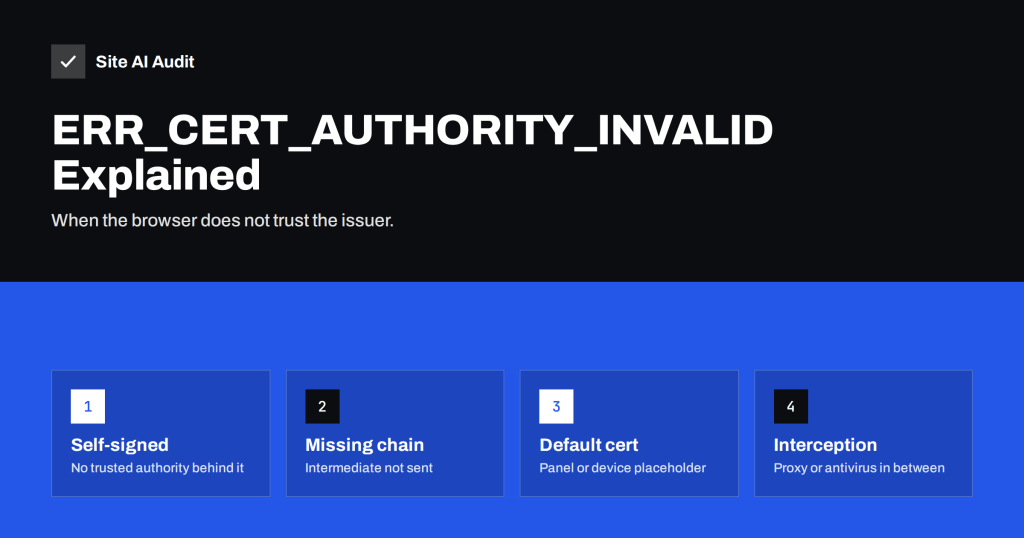
NET::ERR_CERT_AUTHORITY_INVALID: Causes and How to Fix It
ERR_CERT_AUTHORITY_INVALID means the browser does not trust who issued your certificate. Learn how self-signed certificates, chains and proxies cause it.
 2 wrz 2026 · Czas czytania: 8 min
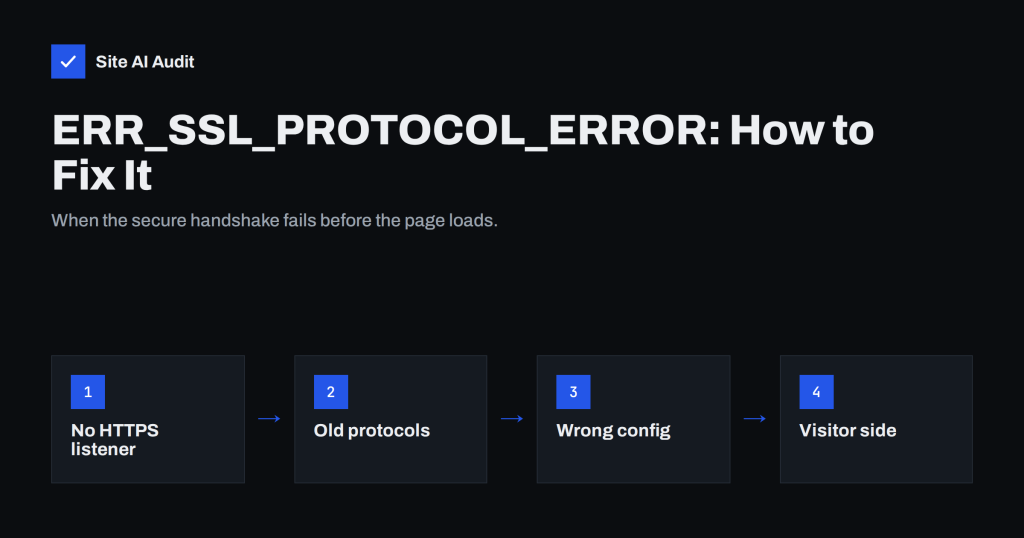
ERR_SSL_PROTOCOL_ERROR: What It Means and How to Fix It
ERR_SSL_PROTOCOL_ERROR means the browser and server could not complete a secure handshake. Learn the causes on the server and visitor side and how to…