 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
#Security headers
Security headers are short instructions a web server sends to the browser with every page. Articles tagged here explain headers such as Strict-Transport-Security, Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy. Each guide describes what the header protects against in plain words. You will find ready-to-adapt examples for Apache, Nginx and common hosting setups. The articles also explain how to roll out a header safely without breaking the site. Read them when an audit reports missing or weak headers.
 15 лист. 2026 р. · Час читання: 8 хв
Security Header Findings: HSTS, CSP, Frame and Referrer Policy
Five small headers harden every page. See how Site AI Audit reports missing HSTS, CSP, frame, referrer and nosniff headers and how to add…
 13 лист. 2026 р. · Час читання: 8 хв
Is Your Website Protected From Hacking? What the Audit Checks
Find security gaps before attackers do. See what the Site AI Audit security check covers, how to read each finding and which fixes to…
 12 лист. 2026 р. · Час читання: 7 хв
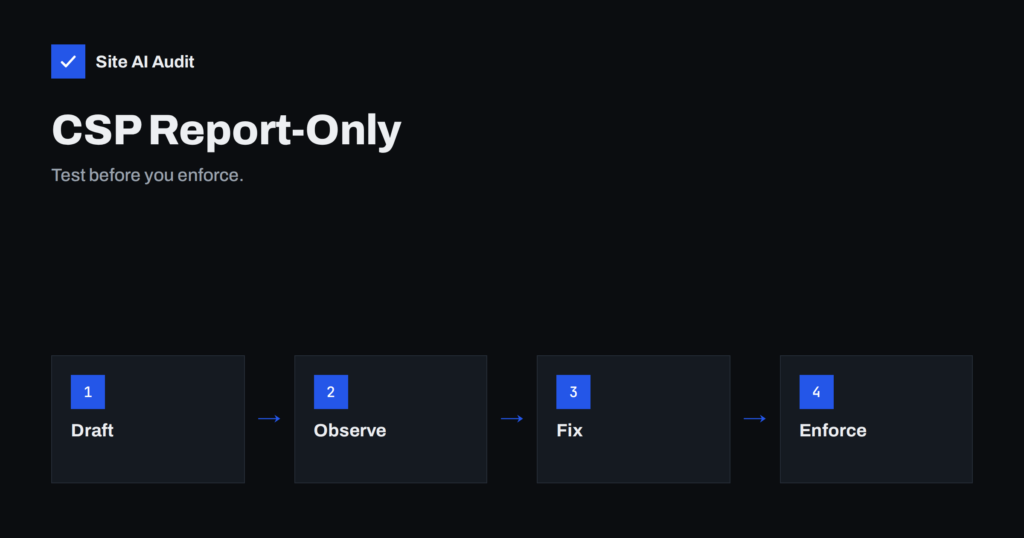
CSP Report-Only Mode: Roll Out a Policy Without Breakage
A strict Content Security Policy can break scripts and styles. Learn how report-only mode lets you test safely, collect violations and tighten the policy.
 9 лист. 2026 р. · Час читання: 8 хв
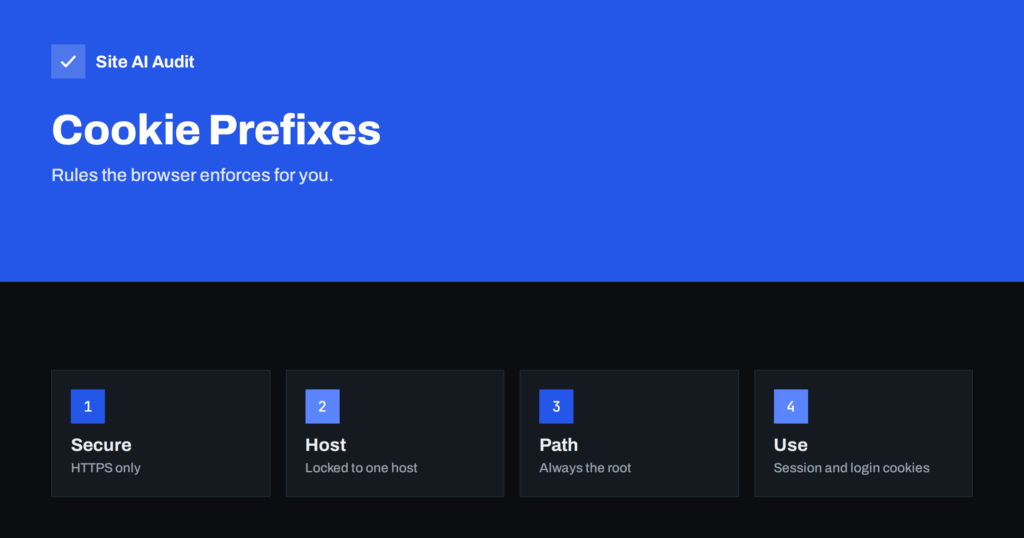
Cookie Prefixes __Host- and __Secure-: Safer Cookie Names
The prefixes __Secure- and __Host- make browsers enforce strict rules on a cookie. Learn what each requires, which cookies to protect and how to…
 6 лист. 2026 р. · Час читання: 8 хв
CRLF Injection: How One Line Break Can Split an HTTP Response
One unchecked line break can let an attacker add headers or cookies to your responses. Learn how CRLF injection works, where it hides and…
 5 лист. 2026 р. · Час читання: 8 хв
Sensitive Data in URLs: Tokens, Emails and Referrer Leaks
Web addresses are copied, logged and sent to other sites unnoticed. Learn why tokens and personal data do not belong in a URL and…
 29 жовт. 2026 р. · Час читання: 8 хв
CORP and COEP Headers: Control Who Loads Your Files
CORP and COEP are two newer security headers that control which sites may load your files. See what they do, when they matter and…
 29 жовт. 2026 р. · Час читання: 7 хв
Embedding Third-Party Iframes Safely: The sandbox Attribute
Iframes bring in maps, videos and forms from other sites, and with them some risk. Learn how the sandbox attribute limits what an embedded…
 20 жовт. 2026 р. · Час читання: 8 хв
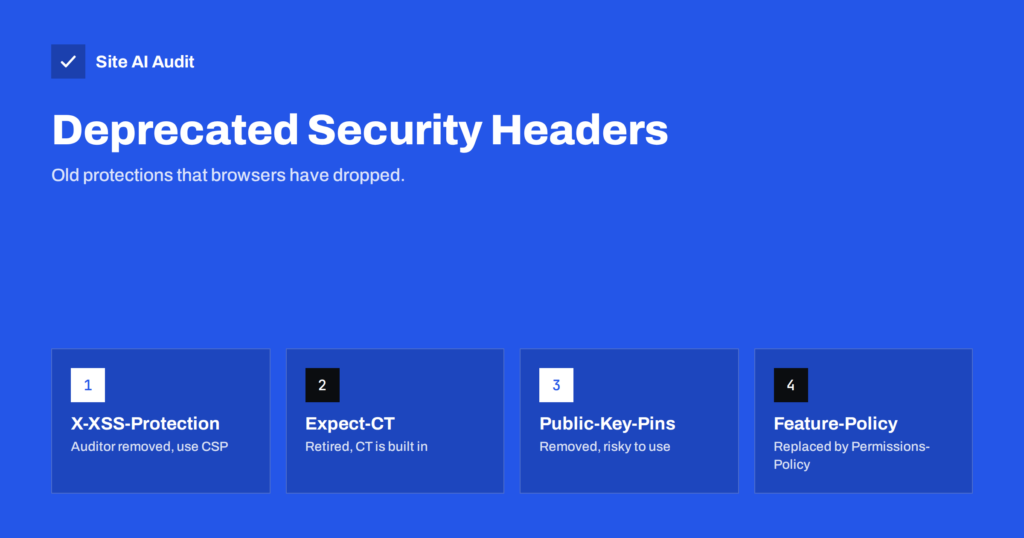
Deprecated Security Headers: X-XSS-Protection, Expect-CT and More
Some security headers are outdated or even harmful today. Learn which ones to remove, which modern headers replace them and how to clean up…
 14 жовт. 2026 р. · Час читання: 7 хв
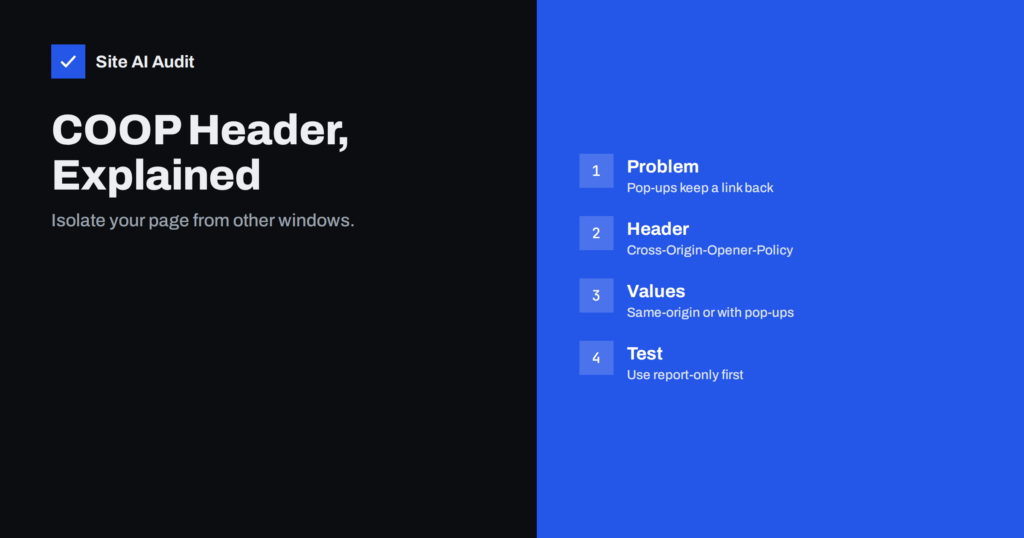
Cross-Origin-Opener-Policy: What COOP Does and When to Use It
COOP is a security header that separates your pages from windows opened by other sites. Learn its values, what it can break and how…
 8 жовт. 2026 р. · Час читання: 8 хв
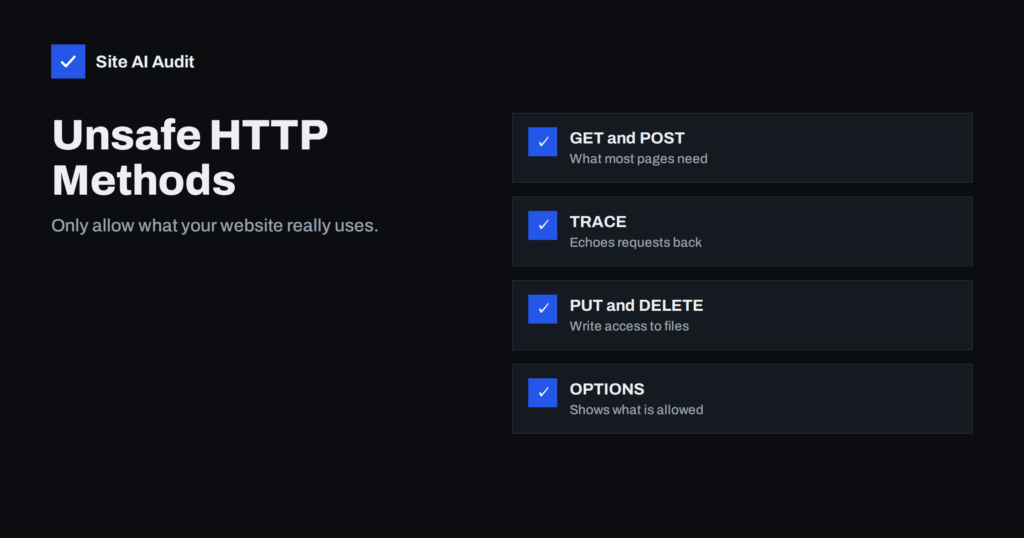
Unsafe HTTP Methods: Why TRACE, PUT and DELETE Should Be Off
TRACE, PUT, DELETE and WebDAV methods left open on a web server can leak data or let attackers upload files. Learn how to test…
 1 жовт. 2026 р. · Час читання: 8 хв
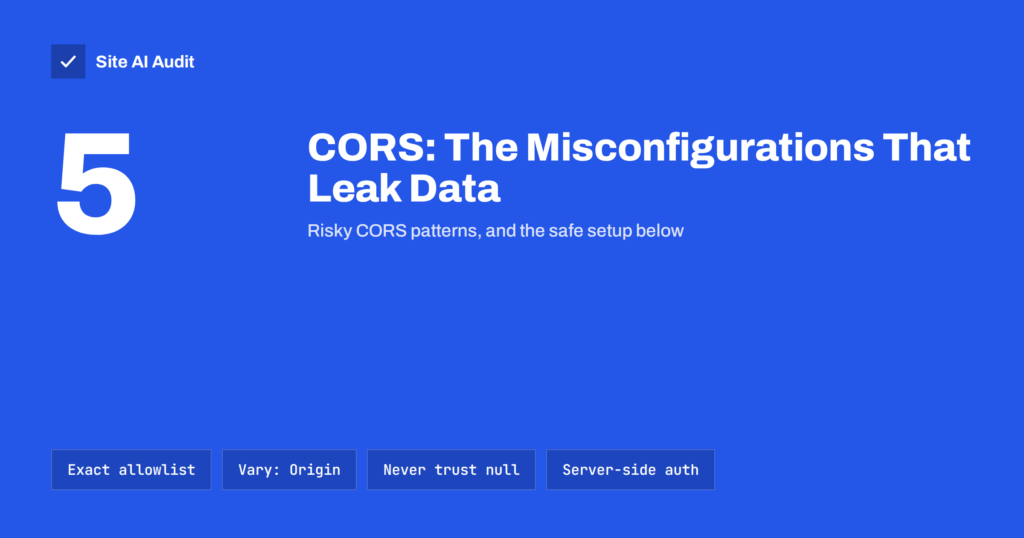
CORS Explained: The Misconfigurations That Expose Your Data
CORS decides which other websites may read your responses. Learn how it works, the common misconfigurations that leak data, and how to set it…