 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
#Website security
Website security covers the everyday measures that keep a site, its visitors and its data safe. Articles tagged here focus on practical protection for small and medium websites rather than enterprise theory. They cover certificates, updates, exposed files, login protection, backups and monitoring. Each guide explains the real risk first and then the fix, in order of impact. The advice fits business owners, marketers, agencies and developers alike. Start here if you want a clear picture of what matters most for your site.
 3 Eki 2026 · 8 dk okuma
Open Redirects: How Attackers Abuse Your Website’s Links
An open redirect lets attackers send visitors from your trusted domain to phishing pages. Learn how to find open redirects and fix them in…
 1 Eki 2026 · 8 dk okuma
SSL Private Keys: How to Store, Protect and Replace Them
Your SSL certificate is only as safe as its private key. Learn where keys should live, who may access them, and what to do…
 1 Eki 2026 · 7 dk okuma
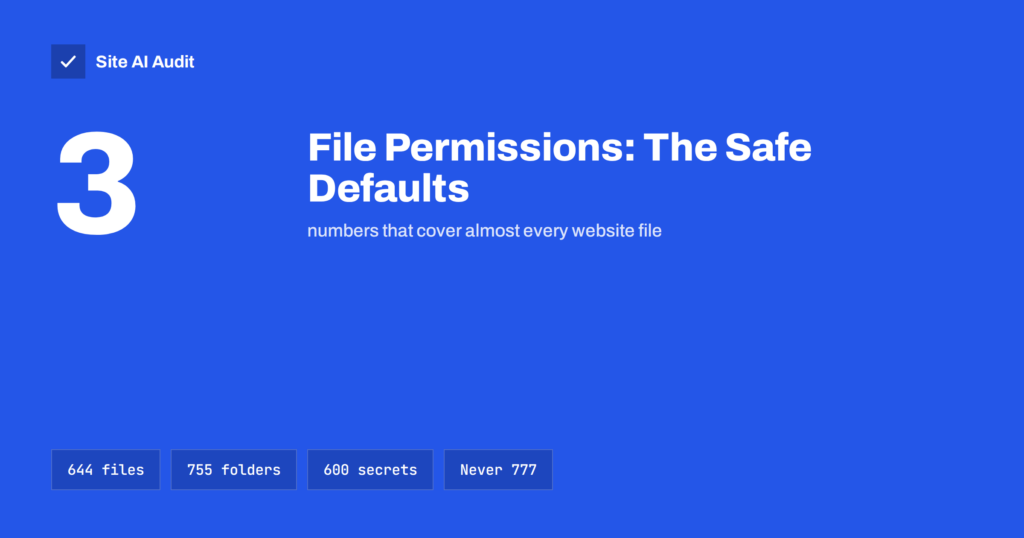
File Permissions on a Web Server: Safe Settings Explained
Wrong file permissions let attackers change your site, while 777 hides deeper problems. Learn what 644, 755 and 600 mean and how to set…
 1 Eki 2026 · 8 dk okuma
Website User Accounts: Least Privilege for Admins and Staff
Too many admin accounts make a website easy to break into. Learn how to set user roles by least privilege, remove old accounts and…
 1 Eki 2026 · 8 dk okuma
CORS Explained: The Misconfigurations That Expose Your Data
CORS decides which other websites may read your responses. Learn how it works, the common misconfigurations that leak data, and how to set it…
 30 Eyl 2026 · 8 dk okuma
DDoS Protection for Small Websites: What You Actually Need
DDoS attacks can take any website offline, but small sites rarely need expensive tools. Learn what DDoS is, which protection matters and how to…
 30 Eyl 2026 · 8 dk okuma
Contact Form Spam: How to Stop Bots Without Losing Leads
Contact form spam wastes time, hides real leads and can harm your email reputation. Learn which layers stop bots without annoying the people who…
 30 Eyl 2026 · 8 dk okuma
Cross-Site Scripting (XSS) Explained for Website Owners
Cross-site scripting lets attackers run their own JavaScript on your pages. Learn the main XSS types, what they can do and how to protect…
 30 Eyl 2026 · 8 dk okuma
SQL Injection Explained: How Sites Get Breached and Protected
SQL injection lets attackers read or change your website's database through a form or URL. Learn how it works, where the risk comes from…
 30 Eyl 2026 · 8 dk okuma
Two-Factor Authentication for Website Owners: What to Protect
Two-factor authentication stops most stolen-password takeovers. See which website accounts to protect first, which 2FA methods to use and how to avoid lockouts.
 29 Eyl 2026 · 8 dk okuma
CSRF Explained: How Cross-Site Request Forgery Works
Cross-site request forgery tricks a logged-in browser into acting on your site. Learn how CSRF works, how tokens and SameSite cookies stop it and…
 29 Eyl 2026 · 8 dk okuma
WordPress xmlrpc.php: What It Does and When to Disable It
WordPress xmlrpc.php is an old remote access door often abused for password guessing and pingback attacks. Learn who needs it and how to block…