 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
#Web vulnerabilities
Web vulnerabilities are weaknesses in websites and web applications that attackers can use to read data, change content or take control. Well-known examples include SQL injection, cross-site scripting, broken access control and outdated software with published flaws. Most of them come from code that trusts user input too much or from components that are no longer updated. They affect small sites built on popular content management systems as much as large custom applications. Understanding the common types helps owners ask the right questions of developers and hosting providers. The articles under this tag explain how the main vulnerabilities work and which practical measures prevent them.
 31 paź 2026 · Czas czytania: 8 min
DNS Zone Transfers (AXFR): Do Not Leak Your Whole DNS
A DNS server that allows zone transfers to anyone hands out your whole record list. Learn what AXFR is, how to test your own…
 30 paź 2026 · Czas czytania: 8 min
Origin Server IP Exposed? How Attackers Bypass Your CDN
A CDN or firewall only protects you while attackers cannot reach your real server. Learn how origin IPs leak and how to lock the…
 30 paź 2026 · Czas czytania: 8 min
Password Reset Flaws: Tokens, Links and Account Takeover
A weak password reset feature lets attackers take over accounts without guessing a password. See the common flaws and how to design a safe…
 30 paź 2026 · Czas czytania: 8 min
Prototype Pollution: A JavaScript Flaw Explained Simply
Prototype pollution lets an attacker change how every object in a JavaScript app behaves. Learn how it works, why it matters and how to…
 29 paź 2026 · Czas czytania: 8 min
CORP and COEP Headers: Control Who Loads Your Files
CORP and COEP are two newer security headers that control which sites may load your files. See what they do, when they matter and…
 29 paź 2026 · Czas czytania: 7 min
Embedding Third-Party Iframes Safely: The sandbox Attribute
Iframes bring in maps, videos and forms from other sites, and with them some risk. Learn how the sandbox attribute limits what an embedded…
 29 paź 2026 · Czas czytania: 8 min
Passkeys for Website Logins: Passwordless Sign-In Explained
Passkeys replace passwords with a key pair stored on the user's device. See how they work, why they resist phishing, and how to roll…
 28 paź 2026 · Czas czytania: 8 min
JavaScript Source Maps Exposed: Is Your Code Public?
Source maps help developers debug minified code, but public ones can reveal your original files. Learn what they expose, how to check and what…
 26 paź 2026 · Czas czytania: 8 min
Email Header Injection: How Contact Forms Get Abused for Spam
Attackers can turn a weak contact form into a spam machine by adding hidden e-mail headers. See how it works and how to protect…
 26 paź 2026 · Czas czytania: 8 min
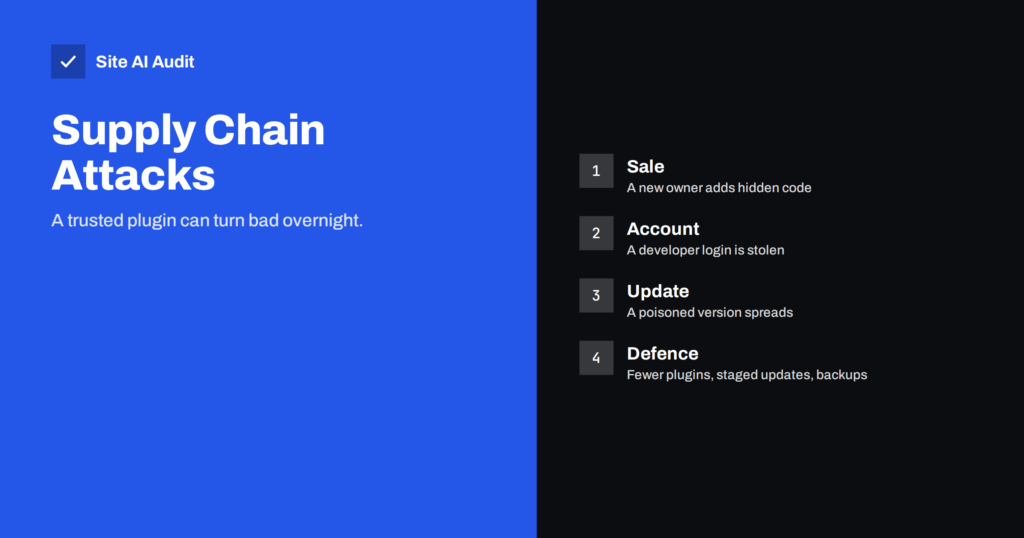
Plugin Supply Chain Attacks: When a Trusted Update Turns Bad
A plugin you trusted can turn harmful after a sale, a stolen account or a poisoned update. See how these attacks work and how…
 25 paź 2026 · Czas czytania: 8 min
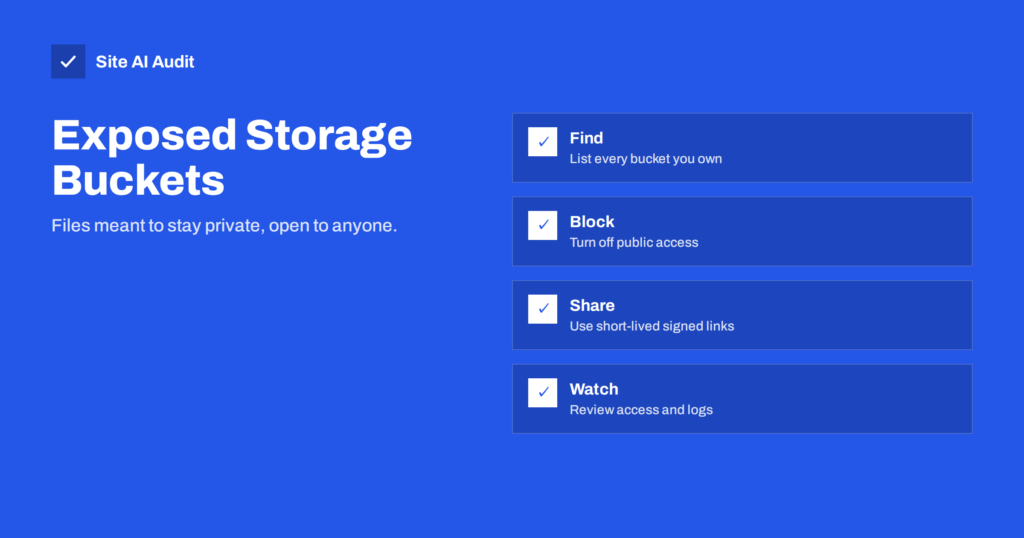
Exposed Cloud Storage Buckets: How Website Data Leaks
Public storage buckets for images, backups and uploads are a common cause of data leaks. Learn how they get exposed, how to check yours…
 25 paź 2026 · Czas czytania: 8 min
Rate Limiting Explained: Slow Down Attackers and Bad Bots
Rate limiting caps how many requests one visitor can make in a set time. Learn where to apply it, how to pick safe limits…