 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
#Security headers
Security headers are short instructions a web server sends to the browser with every page. Articles tagged here explain headers such as Strict-Transport-Security, Content-Security-Policy, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy. Each guide describes what the header protects against in plain words. You will find ready-to-adapt examples for Apache, Nginx and common hosting setups. The articles also explain how to roll out a header safely without breaking the site. Read them when an audit reports missing or weak headers.
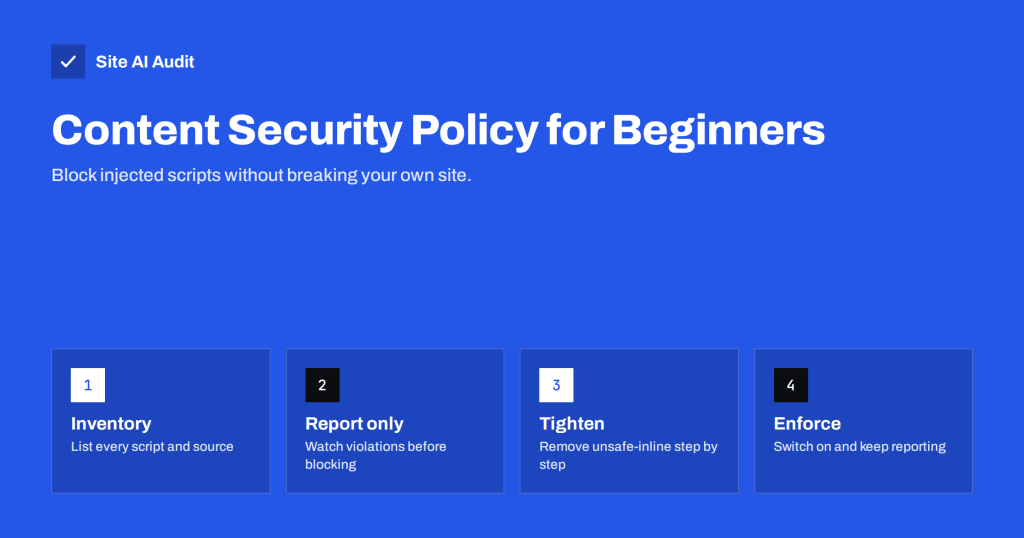 2026. gada 9. aug. · Lasīšanas laiks: 8 min
Content Security Policy for Beginners: A Practical Setup Guide
Content Security Policy blocks injected scripts, but a bad policy breaks your site. Learn the key directives and a report-only rollout that works in…
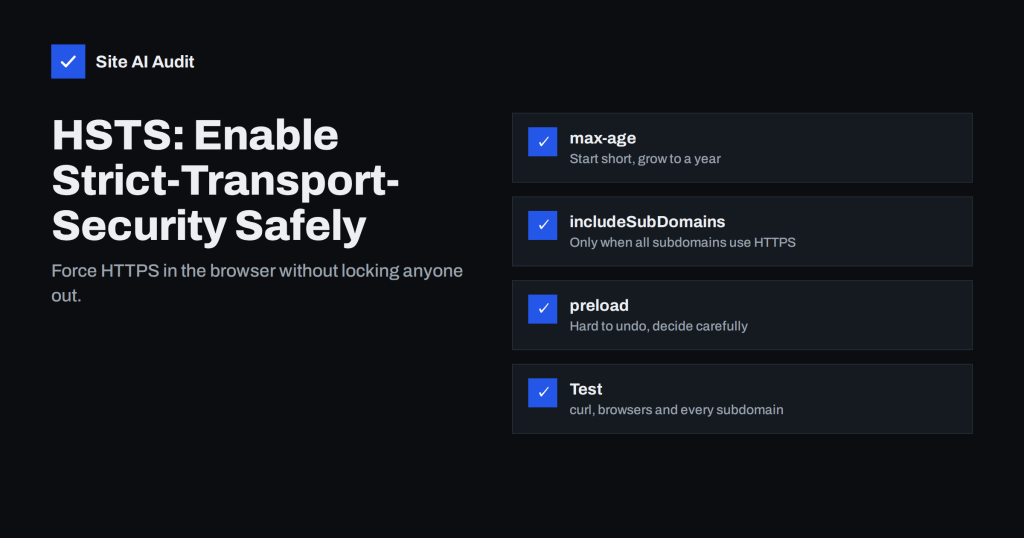 2026. gada 7. aug. · Lasīšanas laiks: 7 min
HSTS Explained: How to Enable Strict-Transport-Security Safely
HSTS makes browsers use HTTPS for your domain every time. Learn what max-age, includeSubDomains and preload mean, and how to roll HSTS out without…
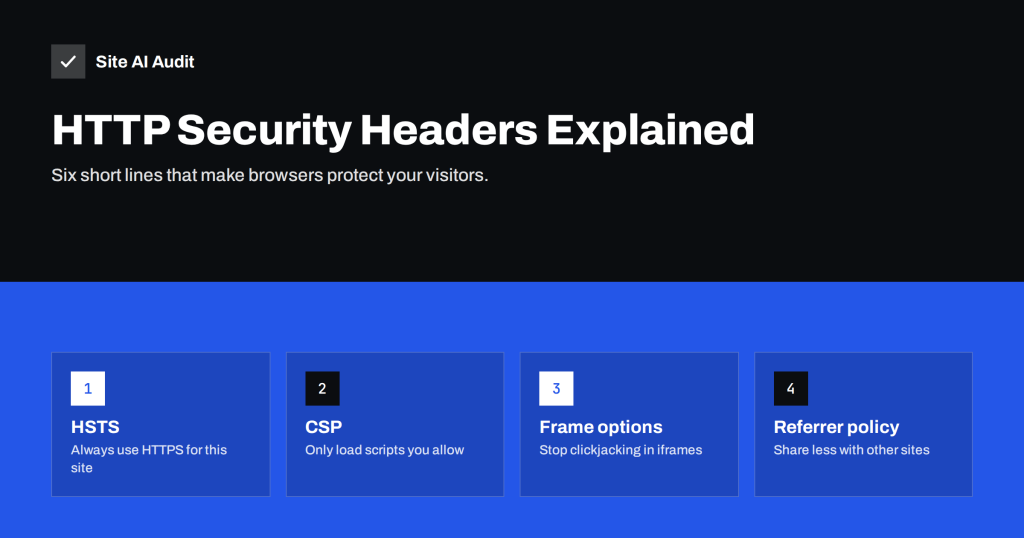 2026. gada 6. aug. · Lasīšanas laiks: 8 min
HTTP Security Headers Explained: What Each One Does
A plain-English guide to HSTS, CSP, X-Frame-Options, X-Content-Type-Options, Referrer-Policy and Permissions-Policy, with safe starting values for each.