 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
セキュリティとSSL
The security basics every website should have, explained without jargon. We cover SSL certificates and their expiry, HTTPS redirects, security headers and software versions that should not be visible. Articles show what visitors see when something is wrong and how browsers warn them away. Each guide gives clear steps you can hand to your host or developer. We also explain how monitoring catches an expiring certificate before customers notice. A safe site protects both your visitors and your search rankings.
 2026/10/25 · 8分で読めます
Rate Limiting Explained: Slow Down Attackers and Bad Bots
Rate limiting caps how many requests one visitor can make in a set time. Learn where to apply it, how to pick safe limits…
 2026/10/24 · 8分で読めます
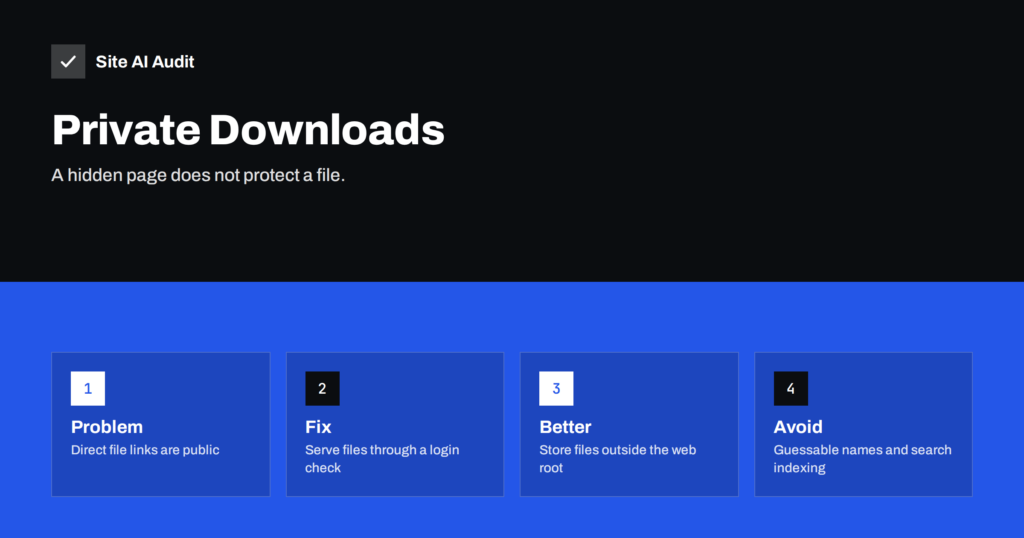
Protecting Private Downloads on a WordPress Website
Files in the WordPress uploads folder are public to anyone with the link, even on a members-only page. Learn how to protect private downloads…
 2026/10/24 · 8分で読めます
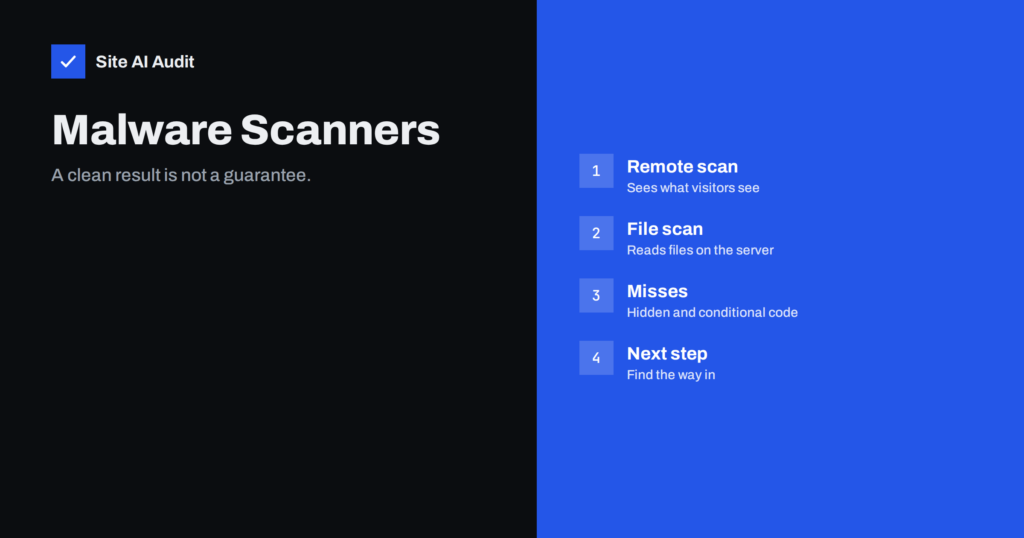
Website Malware Scanners: What They Catch and What They Miss
A clean scan does not always mean a clean website. Learn how malware scanners work, where they fail and what to do next when…
 2026/10/24 · 8分で読めます
WordPress REST API Security: What to Expose and Restrict
The WordPress REST API is on by default and shows more than many owners expect. Learn what it exposes, what can stay public and…
 2026/10/23 · 8分で読めます
Phishing Pages Hosted on Your Website: Find and Remove Them
Attackers often hide fake login pages inside hacked sites. Learn how to spot a phishing page on your domain, remove it safely and prevent…
 2026/10/23 · 8分で読めます
Security Logging and Monitoring: What Small Sites Should Track
Many breaches go unnoticed for months because nobody looks at the logs. Learn which events a small website should record, keep and get alerts…
 2026/10/23 · 8分で読めます
Unrestricted File Upload Vulnerabilities and How to Block Them
A careless upload form can let attackers place a script on your server. Learn how file upload flaws work and the checks that keep…
 2026/10/22 · 8分で読めます
HTTP Request Smuggling Explained for Website Owners
Request smuggling happens when a proxy and a server disagree where one request ends. Learn how it works, what it can lead to and…
 2026/10/22 · 8分で読めます
Server-Side Template Injection (SSTI) Explained Simply
Server-side template injection happens when user input becomes part of a template the server runs. Learn how it works, why it is serious and…
 2026/10/22 · 8分で読めます
JWT Security Mistakes: Protecting Login Tokens on Your Site
JSON Web Tokens are common in logins and APIs, but small mistakes make them easy to forge or steal. Learn the typical flaws and…
 2026/10/21 · 8分で読めます
Web Cache Poisoning Explained for Website Owners
Web cache poisoning tricks your cache into storing a harmful page and serving it to everyone. Learn how it works, where caches are weak…
 2026/10/21 · 8分で読めます
Credential Stuffing: Why Leaked Passwords Threaten Your Site
Credential stuffing uses passwords leaked elsewhere to log in to your site. Learn how it differs from brute force, how to spot it and…