 ENEnglish
 LTLietuviškai
 DEDeutsch
 FRFrançais
 RUРусский
 ESEspañol
 PLPolski
 ITItaliano
 UKУкраїнська
 CSČeština
 PTPortuguês
 JA日本語
 LVLatviešu valoda
 ETEesti
 HUMagyar
 IDBahasa Indonesia
 TRTürkçe
 HIहिन्दी
 ELΕλληνικά
 ARالعربية
 THไทย
 VITiếng Việt
 RORomână
 MSBahasa Melayu
 BNবাংলা
Sicurezza e SSL
The security basics every website should have, explained without jargon. We cover SSL certificates and their expiry, HTTPS redirects, security headers and software versions that should not be visible. Articles show what visitors see when something is wrong and how browsers warn them away. Each guide gives clear steps you can hand to your host or developer. We also explain how monitoring catches an expiring certificate before customers notice. A safe site protects both your visitors and your search rankings.
 18 set 2026 · 8 min di lettura
SSL Certificate Revocation: When and How to Revoke a Certificate
Revoking a certificate tells browsers to stop trusting it before it expires. Learn when revocation is needed, how CRLs and OCSP work and how…
 17 set 2026 · 8 min di lettura
Subdomain Takeover: How Forgotten DNS Records Get Hijacked
A DNS record pointing to a service you no longer use can let attackers take over your subdomain. Learn how subdomain takeover works and…
 16 set 2026 · 8 min di lettura
Subresource Integrity: Protect Your Site From Tampered Scripts
Subresource Integrity lets browsers reject third-party scripts and styles that have been changed. Learn how SRI works, when to use it and where it…
 15 set 2026 · 8 min di lettura
How to Add Security Headers on Apache, Nginx, WordPress and CDNs
Copy-ready examples for adding HSTS, CSP, X-Frame-Options and other security headers on Apache, Nginx, WordPress hosting and CDNs, plus how to verify them.
 14 set 2026 · 8 min di lettura
DNSSEC Explained for Website Owners: Is It Worth Enabling?
DNSSEC signs your DNS records so resolvers can detect forged answers. Learn how it works, what it protects, the risks of misconfiguration and how…
 12 set 2026 · 8 min di lettura
Website Backup Strategy: How to Back Up So You Can Restore
Backups only matter if you can restore them. Learn what to back up, how often, where to store copies and how to test restores…
 11 set 2026 · 7 min di lettura
Web Application Firewall (WAF): Does Your Website Need One?
A web application firewall filters malicious requests before they reach your site. Learn what a WAF blocks, what it cannot do, and which type…
 10 set 2026 · 8 min di lettura
Website Security Scan vs Penetration Test: What You Need
Automated security scans, audits and penetration tests answer different questions at very different costs. Learn what each covers and when you need which.
 9 set 2026 · 7 min di lettura
Brute-Force Login Attacks: How to Protect Your Website Logins
Bots try thousands of passwords on website logins every day. Learn how brute-force and credential stuffing work and which protections actually stop them.
 8 set 2026 · 8 min di lettura
Permissions-Policy Header: Control Camera, Location and More
Permissions-Policy lets you switch off browser features like camera, microphone and geolocation for your pages and embedded iframes. Here is how to set it.
 7 set 2026 · 8 min di lettura
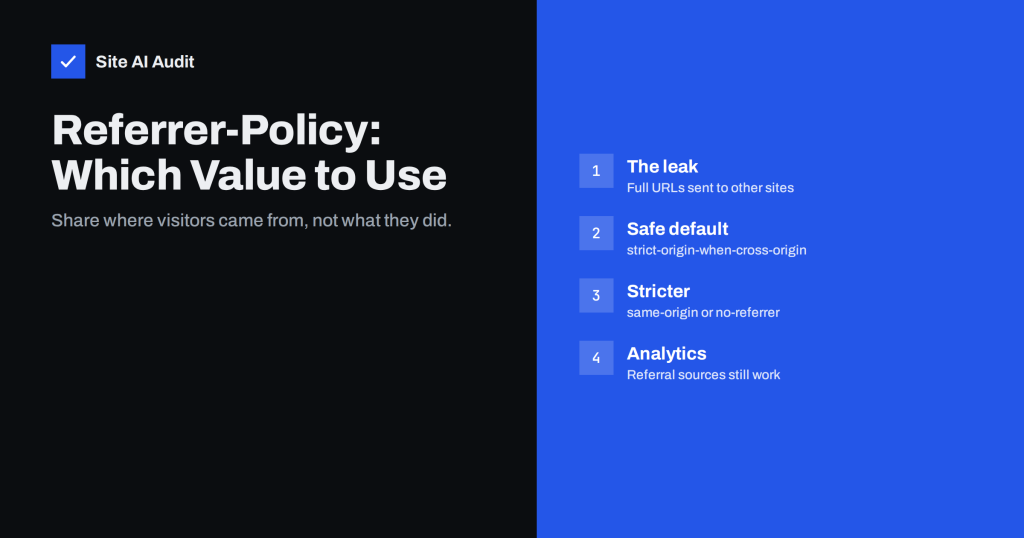
Referrer-Policy Header: Which Value to Use and Why It Matters
Referrer-Policy controls how much of your page URLs other sites see. Learn what each value does, the safe default, and how it affects analytics…
 6 set 2026 · 7 min di lettura
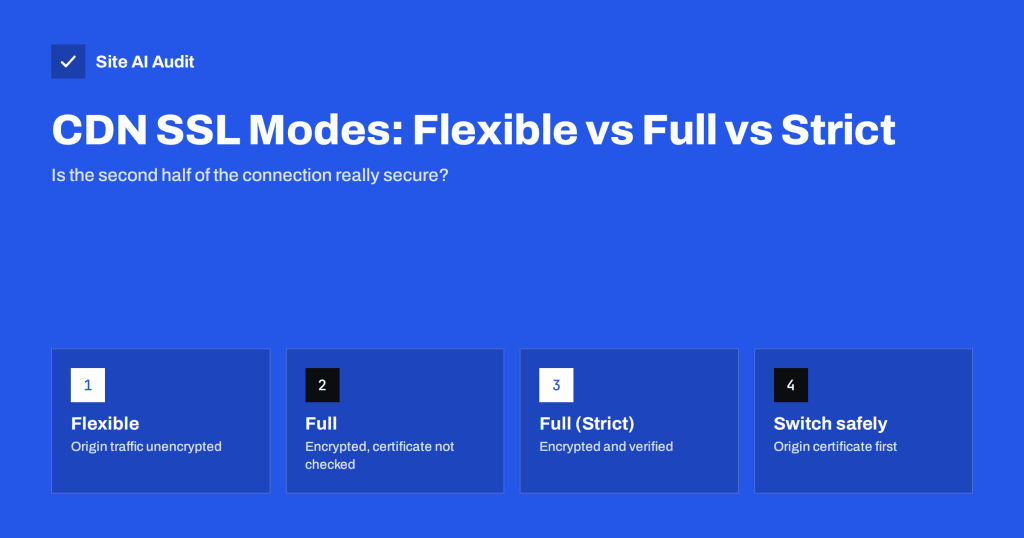
CDN SSL Modes Explained: Flexible vs Full vs Full (Strict)
Flexible, Full and Full (Strict) decide whether traffic between your CDN and server is encrypted and verified. Learn the risks and how to switch…